

artificial intelligence
Google DeepMind AI Agents Expose Flaws in 1024-Bit RSA
Google DeepMind AI Agents Expose Flaws in 1024-Bit RSA
![]() By Elets News Network - 08 November 2026


Google DeepMind said on 6 November 2026 that human-guided AI agents found two weaknesses in legacy 1024-bit RSA encryption: a cheaper way to forge digital signatures and a cheaper way to factor many keys in bulk. Pushmeet Kohli, Vice President of Science at Google DeepMind, said RSA keys of 2048 bits and above are not affected.
It comes weeks after Google gave cyber defenders first access to its Gemini 4 Carbon model. DeepMind researchers Krishnamurthy (Dj) Dvijotham and Abhradeep Thakurta led the project with two well-known cryptanalysts: Nadia Heninger of UC San Diego and Inria, and Emmanuel Thomé of Inria.
What Google DeepMind’s AI agents found in 1024-bit RSA
The results are in two working papers not yet peer reviewed. The first studies an attacker who gets temporary access to a signing device, such as a hardware security module (HSM), and later wants to forge new signatures without ever recovering the private key.
- Padding offers little cover: once an attacker controls roughly half or more of the signed block, the standard PKCS#1 v1.5 padding adds no real difficulty, the paper shows.
- Short digests: for the harder case of a 32-byte digest, the agents proposed a new algorithm that DeepMind estimates is about 1,600 times faster than the previous best attack. That figure is a theoretical estimate, not a completed run.
- Bulk factoring: the second paper describes a batch method that, after a large one-time computation, makes factoring each additional 1024-bit key about 30 times cheaper than earlier batch techniques, again an asymptotic estimate. Its algebra was checked in the Lean 4 proof language.
How much faster is the 1024-bit RSA attack in practice?
The part that actually ran was a rerun of a known benchmark. In September, Laura Shea, Miro Haller, Adam Suhl, Heninger and Thomé forged 1024-bit RSA signatures using an HSM as the signing oracle, a job that took 1,380 CPU core-years over five months. DeepMind says two cooperating AI agents designed, launched and debugged the same computation in under four days and needed 391 core-years, or 3.5 times less CPU time.
The authors credit that gain to better implementation and execution rather than a new algorithm. It still used less than a thousandth of the compute needed to factor the key outright. The finding sits alongside other frontier security models, such as OpenAI’s GPT-6 Cyber, which the company rated Critical for cybersecurity.
Why DeepMind’s RSA research matters for Indian CIOs
The 1024-bit RSA standard has been retired for new signatures for years, but short keys can linger in old HSM configurations, embedded firmware signing, document-signing pipelines and legacy public key infrastructure. Kohli said the work shows organisations should not take the historical “hardness” of cryptographic schemes for granted, and that AI can help defenders raise standards ahead of future threats.
For Indian enterprises already working through CERT-In’s new AI security audit rules with 6-hour reporting, the practical step is an inventory: find every 1024-bit key and raw signing interface still in production and plan migration to 2048-bit or post-quantum schemes. National defenders are also adopting frontier tools, with CERT-In gaining access to Anthropic’s Mythos AI for cyber defence.
Google DeepMind summarised the research in its official post on advancing the frontier of cryptanalysis.
Key takeaways
- Google DeepMind said on 6 November 2026 that human-guided AI agents found two weaknesses in legacy 1024-bit RSA: cheaper signature forgery and cheaper bulk factoring.
- AI agents reran a published 1024-bit forgery in 391 CPU core-years, 3.5 times less than the original 1,380; the 1,600x and 30x gains are theoretical estimates.
- RSA keys of 2048 bits and above are not affected, but CIOs should retire any remaining 1024-bit keys and raw signing interfaces.
FAQ
Does the DeepMind research break RSA-2048 encryption?
No. Both papers say the results do not threaten deployed systems that use 2048-bit or larger RSA keys.
Who led the Google DeepMind cryptanalysis work?
DeepMind researchers Dj Dvijotham and Abhradeep Thakurta led it with cryptanalysts Nadia Heninger and Emmanuel Thomé, and Pushmeet Kohli announced the results on 6 November 2026.
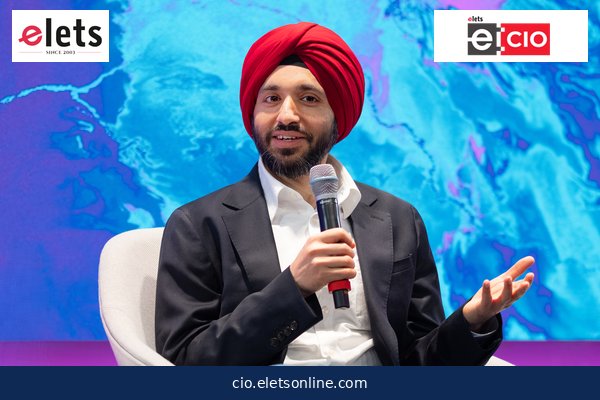
Featured image: Pushmeet Kohli, Vice President of Science at Google DeepMind, speaking in London in June 2026. Photo: Photographer.JuliaMustard / Wikimedia Commons (CC BY-SA 4.0)
Be a part of Elets Collaborative Initiatives. Join Us for Upcoming Events and explore business opportunities. Like us on Facebook , connect with us on LinkedIn and follow us on Twitter.
"Exciting news! Elets technomedia is now on WhatsApp Channels Subscribe today by clicking the link and stay updated with the latest insights!" Click here!